To strengthen subscriber org security, block managed package session IDs from
authenticating anonymous Apex code. If you enable this update, installed managed packages can no
longer use UserInfo.getSessionId() to obtain a session ID and then use the
session ID to execute anonymous Apex.
Where: This change applies to Lightning Experience and Salesforce Classic in Enterprise, Performance, Unlimited, and Developer editions. The release update applies to existing first-generation (1GP) and second-generation (2GP) managed packages.

When: Salesforce enforces this update in Summer ’27. To get the major release upgrade date for your instance, go to Trust Status, search for your instance, and click the maintenance tab.
Why: With this security update, managed package developers must define all Apex classes
in their package metadata so that they can run in subscriber orgs. This change means that managed
package code is versioned, logged, and adheres to access controls. We recommend that managed
packages that must directly interact with subscriber org code do so through standard mechanisms,
such as a shared global interface and Type.forName().
How: To review this update, from Setup, in the Quick Find box, enter Release Updates, and then select Release Updates. For Block Apex Anonymous Code Execution from Managed Packages, follow the testing and activation steps.
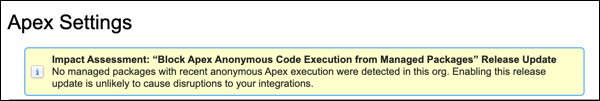
To check if any currently installed managed packages can execute anonymous Apex, go to the Apex Settings page in Setup. Review the note “Impact Assessment: Block Apex Anonymous Code Execution from Managed Packages”. The release update assessment contains either a list of identified managed packages that can execute anonymous Apex, or a confirmation that no managed packages with recent anonymous Apex execution were detected in this org.